BLOG ARTICLE • 07 OCTOBER 2026 • SUGGESTED READING TIME: 10–12 MINUTES
Your perimeter isn’t where it used to be
Your applications and your people no longer sit behind one network edge. Workloads run in your own data centre, in Azure and AWS, and in SaaS. Staff connect from head office, branches, home and the road. If your security still depends on a single firewall at the internet edge, you will have blind spots: traffic you can’t see, policies that drift apart, and little control over what moves between servers inside your network.
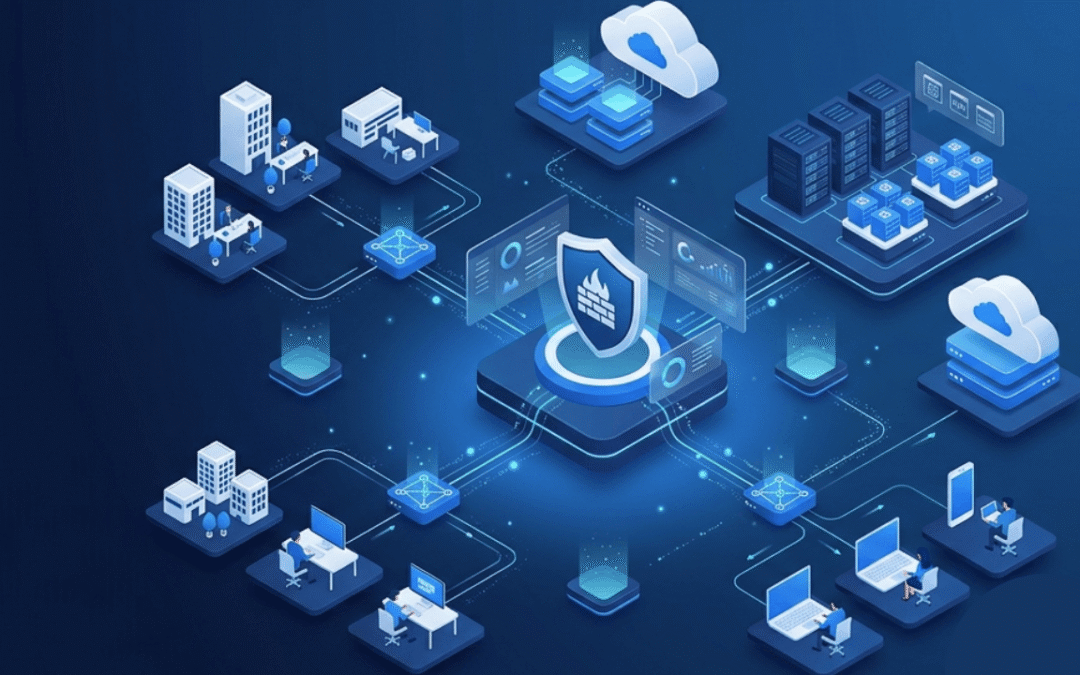
A Hybrid Mesh Firewall (HMF) closes those gaps. It puts hardware, virtual, cloud-native and cloud-delivered firewalls where your traffic actually flows, then runs them as one system with shared policy, shared visibility and central management. Vays Infotech assesses, designs, migrates and runs these environments on Fortinet and Palo Alto Networks.
What is a Hybrid Mesh Firewall?
It is an architecture, and you can’t buy it as a single box. You place enforcement wherever your applications and traffic live, and you manage all of it together, so your team isn’t maintaining a separate rulebase in every environment.
DISTRIBUTED ENFORCEMENT + COORDINATED POLICY + UNIFIED VISIBILITY
- Physical NGFWs at internet edges, branches and data centres
- Virtual and cloud-native firewalls across private/public cloud
- Cloud-delivered Firewall-as-a-Service and remote-user security
- Integrated logging, analytics, automation and policy governance
Why it matters now Applications moved
Your workloads now sit in the data centre, the cloud, SaaS and behind APIs. Security has to go where they go.
Users moved
People work from home, branches and client sites. A rule built around the office IP range no longer covers them.
Traffic patterns moved
Much of your traffic now runs server to server and cloud to cloud, and never crosses the internet edge where your firewall sits.
Operations fragmented
A console per platform, rules that don’t match and logs in different places mean more risk and more work for your team.
The architecture at a glance
| Security layer | Typical deployment | Architectural role |
|---|---|---|
| Physical NGFW | Branch, campus, data centre | Site perimeter and internal segmentation |
| Virtual / cloud firewall | Private cloud, Azure, AWS | Workload, VNet/VPC and ingress/egress protection |
| Cloud-delivered security | Distributed users and branches | FWaaS / secure application and internet access |
| Management and SOC | Shared policy, telemetry and automation | Governance, visibility, response and reporting |
Six things a good design gets right
Multiple enforcement models
Use hardware, virtual, cloud-native or cloud-delivered firewalls according to the path the traffic takes.
Coordinated policy
Write the security intent once and cut duplicate or conflicting rules. How unified this gets depends on what each platform integrates with, and we will tell you where the limits are.
Consistent threat prevention
Apply the same application control, intrusion prevention, anti-malware, DNS and URL filtering at every enforcement point that needs it.
Visibility and telemetry
Give your operations team network, identity, application and workload context in one view.
Automation and APIs
Connect the firewalls to your cloud orchestration, infrastructure-as-code, SIEM, SOAR and ITSM tools, so changes don’t wait on manual tickets.
Identity-aware access
Base access on who the user is, the state of their device and the application they want, as well as IP addresses, wherever the platform supports it.
Hybrid Mesh Firewall on Fortinet
Fortinet markets its firewall portfolio as a Hybrid Mesh Firewall. A typical build uses FortiGate appliances, FortiGate-VM, cloud firewall options and the Fortinet Security Fabric, with central management and analytics on top. What you get in practice depends on the platform, licence and software release you run.
- Branches and data centres: FortiGate NGFW for site perimeter, segmentation and SD-WAN use cases
- Private/public cloud: FortiGate-VM and relevant cloud integrations
- Operations: FortiManager and FortiAnalyzer for central policy, logging and reporting
- Remote users and small sites: FortiSASE for cloud-delivered security
Hybrid Mesh Firewall on Palo Alto Networks
Palo Alto Networks covers the same ground with its Strata network security platform: hardware, software and cloud-delivered firewalls managed together. You can manage them through Panorama or Strata Cloud Manager. The right choice depends on your deployment, so we settle it as part of the design.
- Physical NGFW: PA-Series for perimeter, segmentation and data-centre use cases
- Virtual enforcement: VM-Series for virtualised and cloud environments
- Cloud-native deployment: Cloud NGFW services where available
- Cloud-delivered security: Prisma Access for distributed users and locations
- Management: Panorama or Strata Cloud Manager, depending on your deployment model
Fortinet or Palo Alto Networks? Start with requirements.
Decide where you need enforcement, how your team will run it and how you will migrate before you shortlist products. Throughput figures and appliance datasheets are a poor basis for choosing either vendor. If your parent company has already set a global standard, we design within it.
| Assessment area | Questions to resolve |
|---|---|
| Network and branch | Sites, internet circuits, SD-WAN, VPNs, HA, routing |
| Data centre and applications | East–west flows, application dependencies, TLS inspection, segmentation |
| Cloud and SaaS | Azure/AWS workloads, ingress/egress, VPC/VNet traffic, cloud-to-cloud flows |
| Identity and users | Entra ID/SSO, ZTNA, remote access, device posture |
| Security operations | SOC/SIEM integration, logs, alert workflows, platform skills |
| Governance and commercial | Policy ownership, CERT-In log retention, DPDP obligations, subscriptions, 3-year TCO |
This is more than a firewall refresh
If you swap an appliance without looking again at your traffic, you carry the old rule clutter onto new hardware. Ask four questions first. Where will your applications run in three years? Which traffic never passes through the corporate gateway? Which rules are duplicated? Can your team see what is happening in the cloud and between servers?
An example: a distributed enterprise
Take a company with a head office, 20 branches and plants, a private data centre, workloads in Azure, Microsoft 365 and staff who travel. One workable design puts hardware NGFWs at the main sites, virtual and cloud-native firewalls around the workloads, cloud-delivered security for remote access, and one monitoring layer across all of it. You may not end up with fewer firewalls. You end up with firewalls that work as one system.
How Hybrid Mesh relates to Zero Trust and SASE
The three fit together, and none replaces another. HMF decides where firewall controls sit and how they are coordinated. Zero Trust adds continuous access decisions based on identity, device, application and risk. SASE joins networking and cloud-delivered security for users and sites spread across locations.
How Vays Infotech helps
01 Current-state discovery
We inventory your firewalls, software versions, interfaces, zones, routing, NAT, VPNs, HA pairs, subscriptions, log flows and connected services.
02 Rulebase and policy assessment
We find redundant, over-permissive, shadowed and legacy rules, then confirm with application owners what each remaining rule is for.
03 Application and traffic mapping
We map how users reach applications and how applications talk to each other, including cloud and third-party dependencies.
04 Target architecture and platform selection
We define firewall form factors, where they sit, how you segment, how you manage and monitor them, and which vendor fits.
05 Migration and implementation
We translate policy, write test cases, sequence each cutover and prepare rollback, so the business keeps running through the change.
06 Optimisation and managed operations
After go-live we tune policy and can run monitoring, patching, governance reporting and incident response for you.
Hybrid Mesh Firewall Readiness Assessment
Before you issue a firewall RFQ, find out what you actually need. Our structured assessment tells you where enforcement belongs and how your team will operate it. You receive:
- Current-state architecture and firewall inventory
- Rulebase, traffic and application-dependency assessment
- Cloud, branch, remote-user and segmentation requirements
- Target-state Hybrid Mesh Firewall architecture
- Fortinet / Palo Alto Networks technology mapping
- Implementation roadmap, risks and indicative bill of materials
Secure the network you have and the one you are building
Your applications, users and workloads are spread out, and your security design should match. Vays Infotech is a Bengaluru-based systems integrator and managed services provider. We plan and build practical Hybrid Mesh Firewall architectures for branches, data centres, cloud and remote workers.
Editorial references
Fortinet – Hybrid Mesh Firewall
Fortinet – Hybrid Mesh Firewall overview:
Palo Alto Networks – Strata Cloud Manager documentation
Gartner – Hybrid Mesh Firewall research (licensing/access may apply):
Editorial note: Confirm current OEM feature availability, licensing, regional availability and supported management integrations before publication or proposal commitment. Also confirm Vays partner tiers and office locations, check the CERT-In and DPDP wording with compliance, and clear any Gartner reference against Gartner’s citation policy.